Content Tagged “security”
-
The Whole Story Behind PHP2Shell
At the end of 2006, PHP security expert Stefan Esser left the PHP Security Team1. That was almost twenty years ago. Esser left because he said he “found it impossible to improve PHP security from within”. Any kind of critical discussion of PHP’s security model would cause one to be shunned by the other developers, he said. Instead of making the software better, people in the project would concentrate on semantics, calling him rude and then ignoring his fixes, Esser reported. He left the project in frustration.
As it turns out, in 2004, Esser had found one of the underlying problems that would later cause the PHP2Shell debacle. In July of that year, he reported on a fix for it. But that, obviously, wasn’t the whole story. As it turns out, the security research company Esser works for now, Calif.io, kept at it and actually discovered the new vulnerabilities in August of this year — apparently shortly before their rival hackers from Wiz did. Here’s the full write-up on the Calif site. Yes, security vulnerabilities have comics now. 🫣
How did we find this?
No special harness, or access to models that weren’t generally available to everyone were used in the initial bug discovery. I focused on something I had a background in, knew its vulnerability history well, and held a theory that specific bugs lurk within the codebase. This shows that “know your target” is still as applicable as ever, even in the LLM dominated VR age. No model is simply capable of unearthing “all bugs” with simple prompts. At least for now.
-
The Security Situation at PHP
I’m really glad I stopped using PHP years ago. You really wouldn’t want to be caught running it right now. Not only because of PHP2Shell, that seems to be only the tip of the proverbial iceberg. This is from the PHP projects offical news release on that monumental security issue:
In 2024, PHP underwent its first external security audit in years. The PHP Foundation secured funding from the Sovereign Tech Agency to organize this audit through OSTIF, and it was carried out by Quarkslab. While fixing one of the issues Quarkslab reported, a PHP core developer contracted by the PHP Foundation found the first signs of the OOM problem behind CVE-2026-109618. In 2024, a potential exploit for the OOM problem was theorized, but no concrete vectors were found and other concrete issues with clear impact overshadowed these concerns.
Why doesn’t this project have regular external security audits? It runs 70% of the web, for fuck’s sake! And what do you mean you knew of this problem two years ago but couldn’t figure it out? What are the chances that other people did and just didn’t tell you? I am now almost completely convinced that these vulnerabilities must have been exploited as zero days for years. This is an absolute disaster for this project.
To fix the OOM problem, the PHP security team developed several competing approaches, but each came with its own trade-offs: backward compatibility breaks, new denial-of-service potential, or requiring changes to many third-party extensions which seemed impossible to coordinate. The PHP security team, operating on consensus, struggled to choose between these and feared the repercussions of shipping the wrong choice. Combined with the lack of a known path to remote code execution and the small team of core developers with the necessary deep knowledge of the engine occupied with many responsibilities, this decision process caused work on a fix to stall and restart repeatedly over months. We won’t pretend otherwise: the delay was a structural failure, caused by both the security team’s decision process and its lack of resources. The security team has since started changing its processes, and that work continues, so that decisions can be made by majority and compromises are encouraged.
Maybe give your security team more resources then? Nah, features have always been more important than security to these guys. Let’s face it. People … stop using PHP!
Thanks to John Chandler, who alerted me to this post by the PHP people!
-
The Boston Scientific Hack
Two weeks ago, it became known that Boston Scientific, a major medical device manufacturer from the US that produces lab equipment and many devices used to treat heart conditions, was hacked. To this day, we do not know what happened at the company. Their press releases on the matter include no information whatsoever about what this “cybersecurity incident” actually was. The infamous US infosec services provider CrowdStrike is involved in investigating this attack, but hasn’t given any details either. “Cyber attack” always sounds very sinister, but what this most often boils down to is an employee at the company getting duped into executing malware from somewhere in the cloud or brought in on a local storage device. In the more sophisticated attacks, the “supply chain” of some software they used is attacked, which often means some developer let his GitHub credentials get out and someone modified some software without anyone noticing.
Speaking of supply chains, this situation has apparently now led to hospitals desperately counting their catheters and stents because Boston Scientific doesn’t know when they can ship more product. Aren’t just-in-time supply chains great! 😥
But there are other serious consequences, as The Register reports:
Medical-device maker Boston Scientific, whose IT systems were hacked by unknown intruders last week, said the cyberattack remains ongoing. It also noted that pacemakers and other heart devices implanted after the August 25 breach cannot provide remote monitoring and data transmission as intended. “New remote monitoring communicators cannot be activated, thus available device data will NOT be transmitted to remote patient management systems until the communicator can be activated,” the medtech firm said in a late Friday update.
This applies to all new cardiac rhythm management implants other than insertable cardiac monitors (ICM). ICM devices must be activated using the Boston Scientific Clinic Assistant app to ensure the device correctly records patients’ heart rhythms, the company added. Because of the cyberattack, “new ICMs are unable to pair to the patient remote monitoring mobile phone, therefore available episode data recorded by the ICM will NOT be transmitted to the remote monitoring system until the ICM can be paired to the patient mobile app,” according to the update. The devices will still record any episodes, and patients can transmit these to the remote monitoring system by in-person transmission via the Clinic Assistant app. This is done by selecting the “interrogate” button, according to the company.
When will these people realise that our whole digital infrastructure is built on sand? Somebody executes some code or loses the credentials to a source code management system somewhere and, next thing you know, a whole company stops functioning, critical devices don’t work anymore and hospitals are left without life-saving supplies. What happened to having emergency stocks of vital consumables? And why do we rely on software and protocols for critical medical devices that any sixteen-year-old with access to Claude Code can hack while they’re in an Apex Legends match at the same time?
-
Mikko’s SMP
Mikko Hyppönen, famed IT security researcher and longtime head of research at F-Secure, has been wearing an Omega Seamaster Professional original blue wave dial “Bond Watch” as a daily driver for 25 years now. His is a few years ahead of mine and the full-size version, and he’s rocking the original bracelet, but he’s basically my brother-in-watch. And, unsurprisingly, the man who coined Hyppönen's Law of IoT Security (“whenever an appliance is described as being ‘smart’, it is vulnerable”) likes his mechanical watch for the same reason I like mine, too:
I’ve been carrying the same watch for 25 years. It’s an Omega Seamaster Professional. This is not a smartwatch. No wifi, no bluetooth, no chipset. Can’t be hacked.
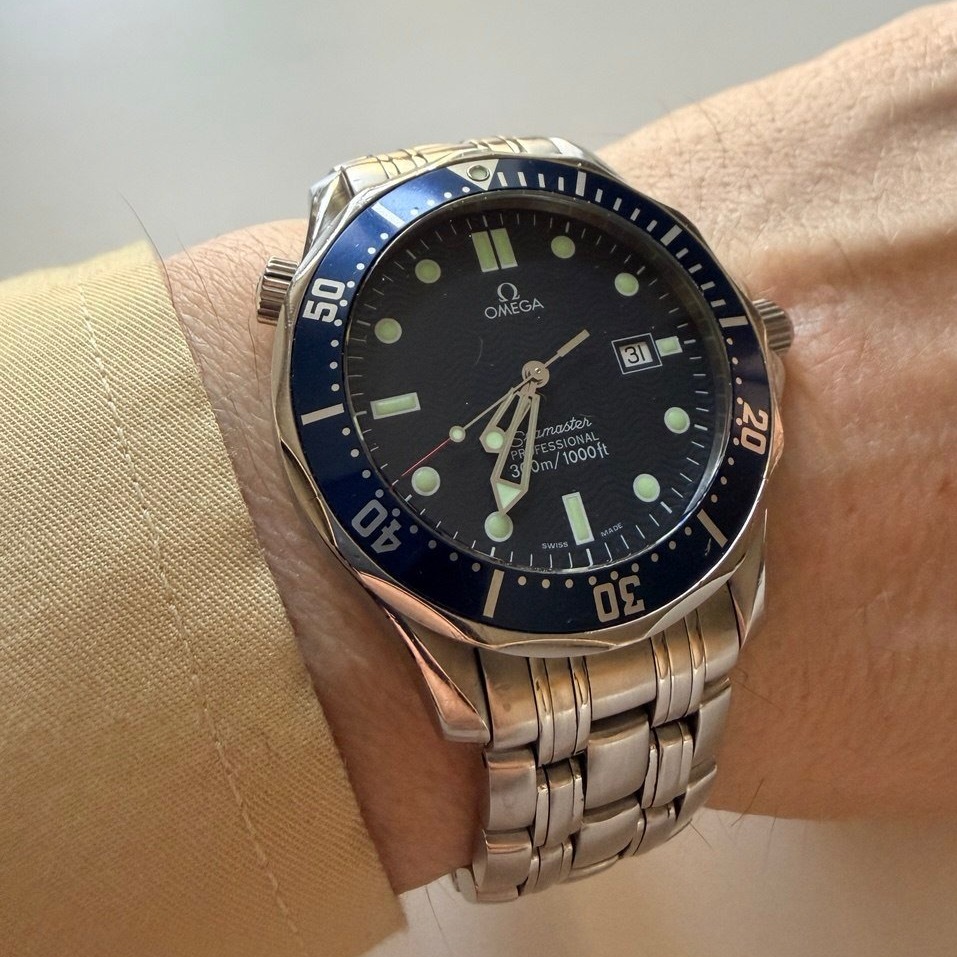 Mikko Hyppönen’s Omega Seamaster Professional (Photo: Mikko Hyppönen)
-
The Horrible Cambodian Scam Industry
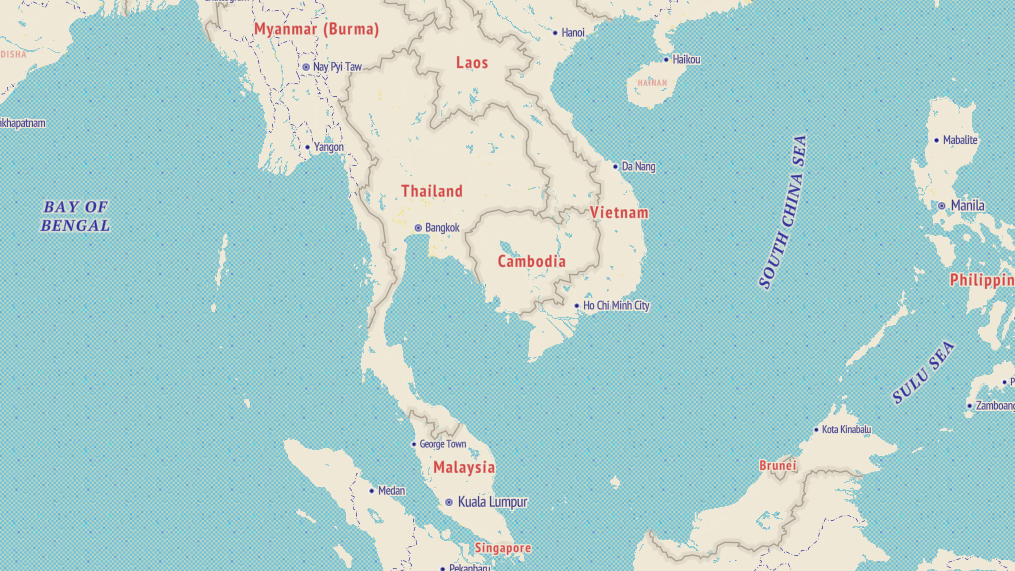 Cambodia within South East Asia (Mapping by Mapbox)
Ever wondered where all that spam comes from? Man, this is bad.
→ Reuters: Amnesty says Cambodia is enabling brutal scam industry
Human rights group Amnesty International accused Cambodia’s government on Thursday of “deliberately ignoring” abuses by cybercrime gangs that have trafficked people from across the world, including children, into slavery at brutal scam compounds. The London-based group said in a report that it had identified 53 scam centres and dozens more suspected sites across the country, including the Southeast Asian nation's capital, Phnom Penh.
The prison-like compounds were ringed by high fences with razor wire, guarded by armed men and staffed by trafficking victims forced to defraud people across the globe, it said, with those inside subjected to punishments including shocks from electric batons, confinement in dark rooms, and beatings. Amnesty said its findings revealed a "pattern of state failures" that allowed the billion-dollar industry to flourish, including failures to investigate human rights abuses, identify and assist victims, and regulate security companies and tools of torture.
-
What I’ve Been Up To
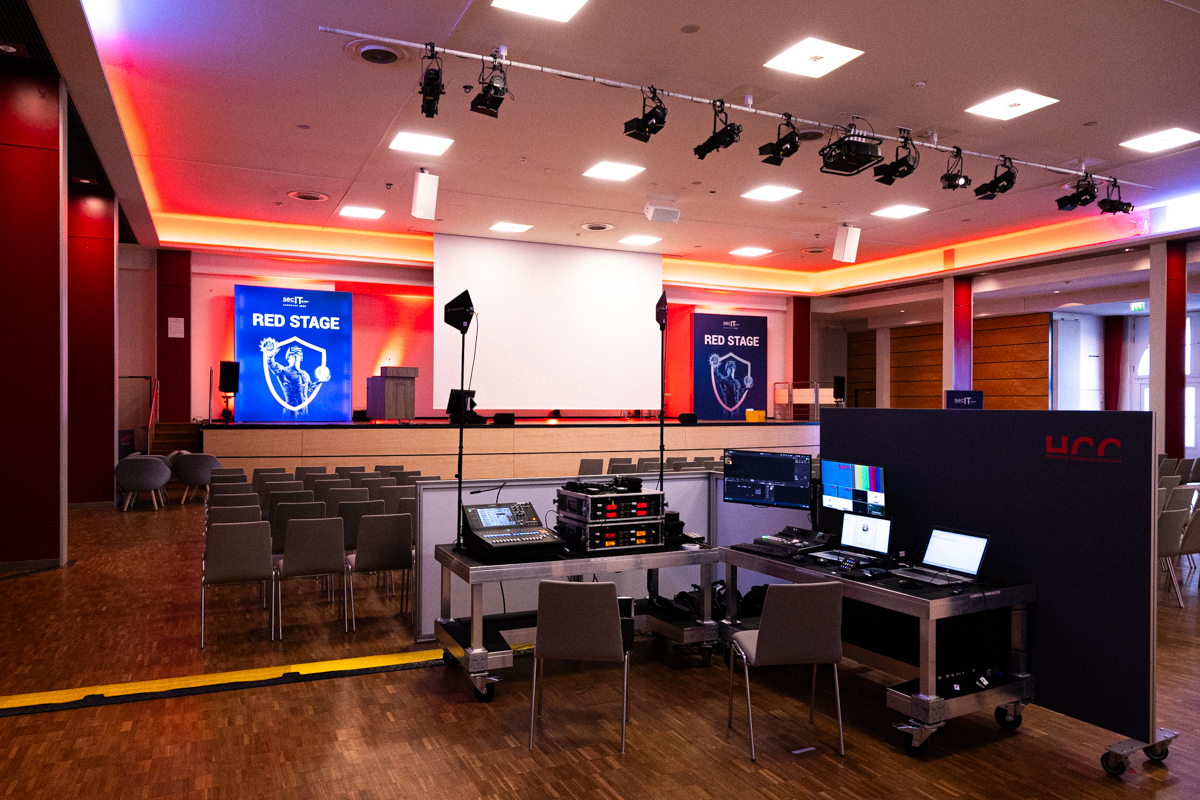
You’ve probably noticed that there hasn’t been much going on here lately. This is mostly because I’ve been working very hard behind the scenes to bring the website up to version 3.0, which includes a visual refresh for the site’s theme. I’ve also spent a week on the road, hosting a stage at the secIT 2025 conference as well as doing a lot of networking and sourcing for stories around the event.
I then promptly got the obligatory conference flu, which laid me out for about a week. I completely lost my voice for a few days and was also very tired, the combination of which prevented me from getting any work done. So naturally, there is now quite a backlog to get through.
The work on the new website version is still ongoing behind the scenes. This refresh is made up of three new colour schemes that took me a few weeks to nail down. There are also new features which had to be implemented and tested properly. That’s all finished now. But there is still a lot of work to be done, because I’ve had to touch every single piece of content on the site to change some code that has to do with a new, improved categorisation scheme that’s part of the new design. It’s a lot of work, but will be well worth it in the end. I hope I’ll have that completed soon, so that everyone gets to see the new version of the site that I’ve been working on. Until then, hang tight.